Description
Full Service Description
ISO/IEC 27001 is the internationally recognized standard for establishing, implementing, maintaining, and continually improving an Information Security Management System (ISMS). Certification by an accredited certification body provides independent assurance that an organization’s ISMS complies with the requirements of ISO/IEC 27001:2022 and is operating effectively.
Make Audit Easy delivers ISO/IEC 27001 External Audit & Certification Services through the Make Audit Easy platform. As an accredited certification body, we conduct independent, impartial, and internationally recognized certification audits in accordance with ISO/IEC 17021-1 and applicable accreditation requirements.
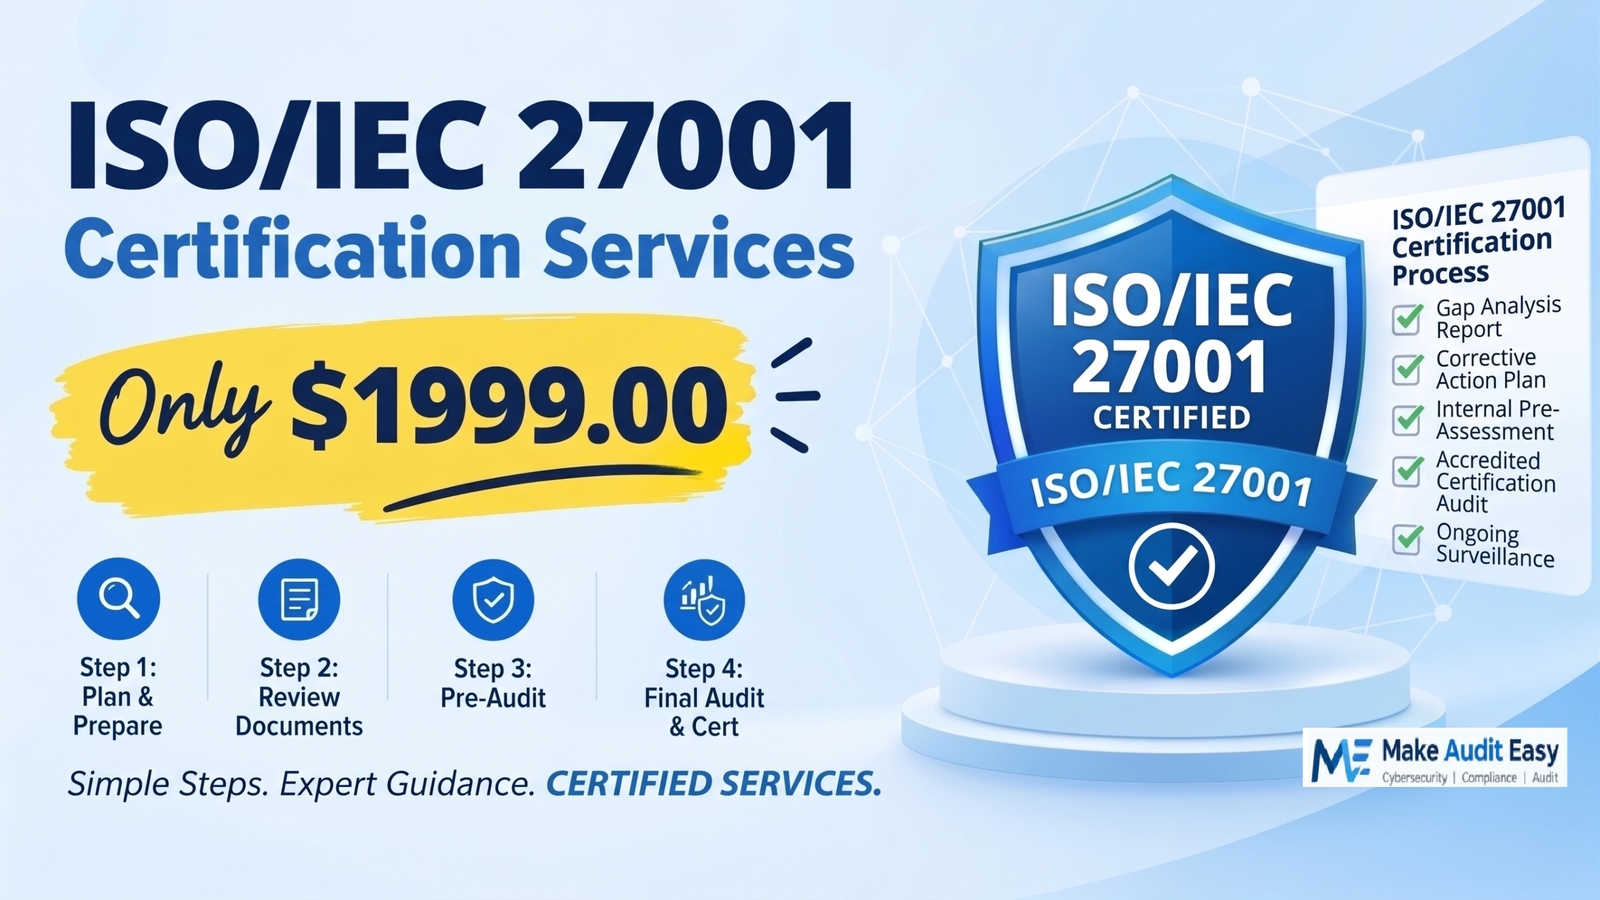
Our certification process includes Application Review, Stage 1 Audit (Documentation & Readiness Review), Stage 2 Certification Audit (Implementation & Effectiveness Assessment), certification decision, and issuance of the accredited ISO/IEC 27001 certificate upon successful completion of the certification process.
Our experienced certification auditors evaluate compliance with all applicable ISO/IEC 27001:2022 clauses and Annex A controls, verify the effectiveness of the Information Security Management System, assess risk management practices, and confirm continual improvement of the ISMS.
Organizations achieving certification demonstrate internationally recognized information security practices, strengthen customer confidence, satisfy regulatory and contractual requirements, and enhance their competitive position in the marketplace.
Key Audit Coverage
-
Application and contract review
-
Stage 1 documentation audit
-
Stage 2 certification audit
-
ISMS scope and organizational context
-
Leadership and governance
-
Information security risk management
-
Statement of Applicability (SoA)
-
Annex A control implementation
-
Operational effectiveness of security controls
-
Internal audits and management reviews
-
Corrective actions and continual improvement
-
Certification decision and certificate issuance
Who This Service Is For
-
Organizations seeking first-time ISO/IEC 27001 certification
-
Organizations upgrading to ISO/IEC 27001:2022
-
Businesses requiring accredited certification for customers, regulators, or contracts
-
Organizations demonstrating internationally recognized information security compliance
-
Enterprises operating single-site or multi-site ISMS environments
Outcome
An independent accredited certification confirming that your Information Security Management System complies with ISO/IEC 27001:2022, providing internationally recognized assurance of your organization’s commitment to information security, regulatory compliance, and continual improvement.
Reviews
There are no reviews yet.